
Prudence: security and governance
Built for regulated finance. Open about what comes next.
Ministries, development banks and boards need to know exactly what a system does today. This page separates what is live from what is still on the roadmap.
Live Operational today
- Role-based access control
- Six roles (CGS Admin, Maker and Checker; bank Admin, Maker and Checker). Every server route checks who is asking, and automated tests sweep them route by route.
- Four eyes
- Every claim, disbursement and recovery decision, and every application and report the scheme reviews, needs a second person, and the system checks it is a different person, not only a different role. Work completed automatically is sampled by weekly random checks.
- Audit trail
- Every decision records who made it, when, and the document behind it. Audit entries cannot be edited by the application, the CGS Admin or the vendor. Boards and auditors can see the history of every decision.
- Leverage ceiling enforcement
- Can be switched on for any scheme. When it is on, approvals are blocked at the leverage ceiling, at the point of approval rather than after the fact, and no user can override it. A decision that would increase the scheme's exposure, such as continuing cover on a restructured loan, goes to the credit committee.
- Three-tier settings hierarchy
- Platform, scheme and institution-agreement settings are kept separate, so one institution's configuration never affects another's.
- Per-loan reconciliation record
- Every reconciliation leaves a permanent record for each loan: the scheme's computed figure, the institution's reported figure and the approved settlement basis.
Roadmap Not yet built
- Core banking integration
- API endpoints and webhooks so institutions' core banking systems can send data automatically instead of through the portal.
- Regional and multi-country schemes
- Now being introduced: one deployment for a regional body, with each country's scheme kept separate and a Regional Admin allocating capital from the regional fund.
Detailed security documentation is available to evaluators on request.
In the platform
Controls you can see on screen.
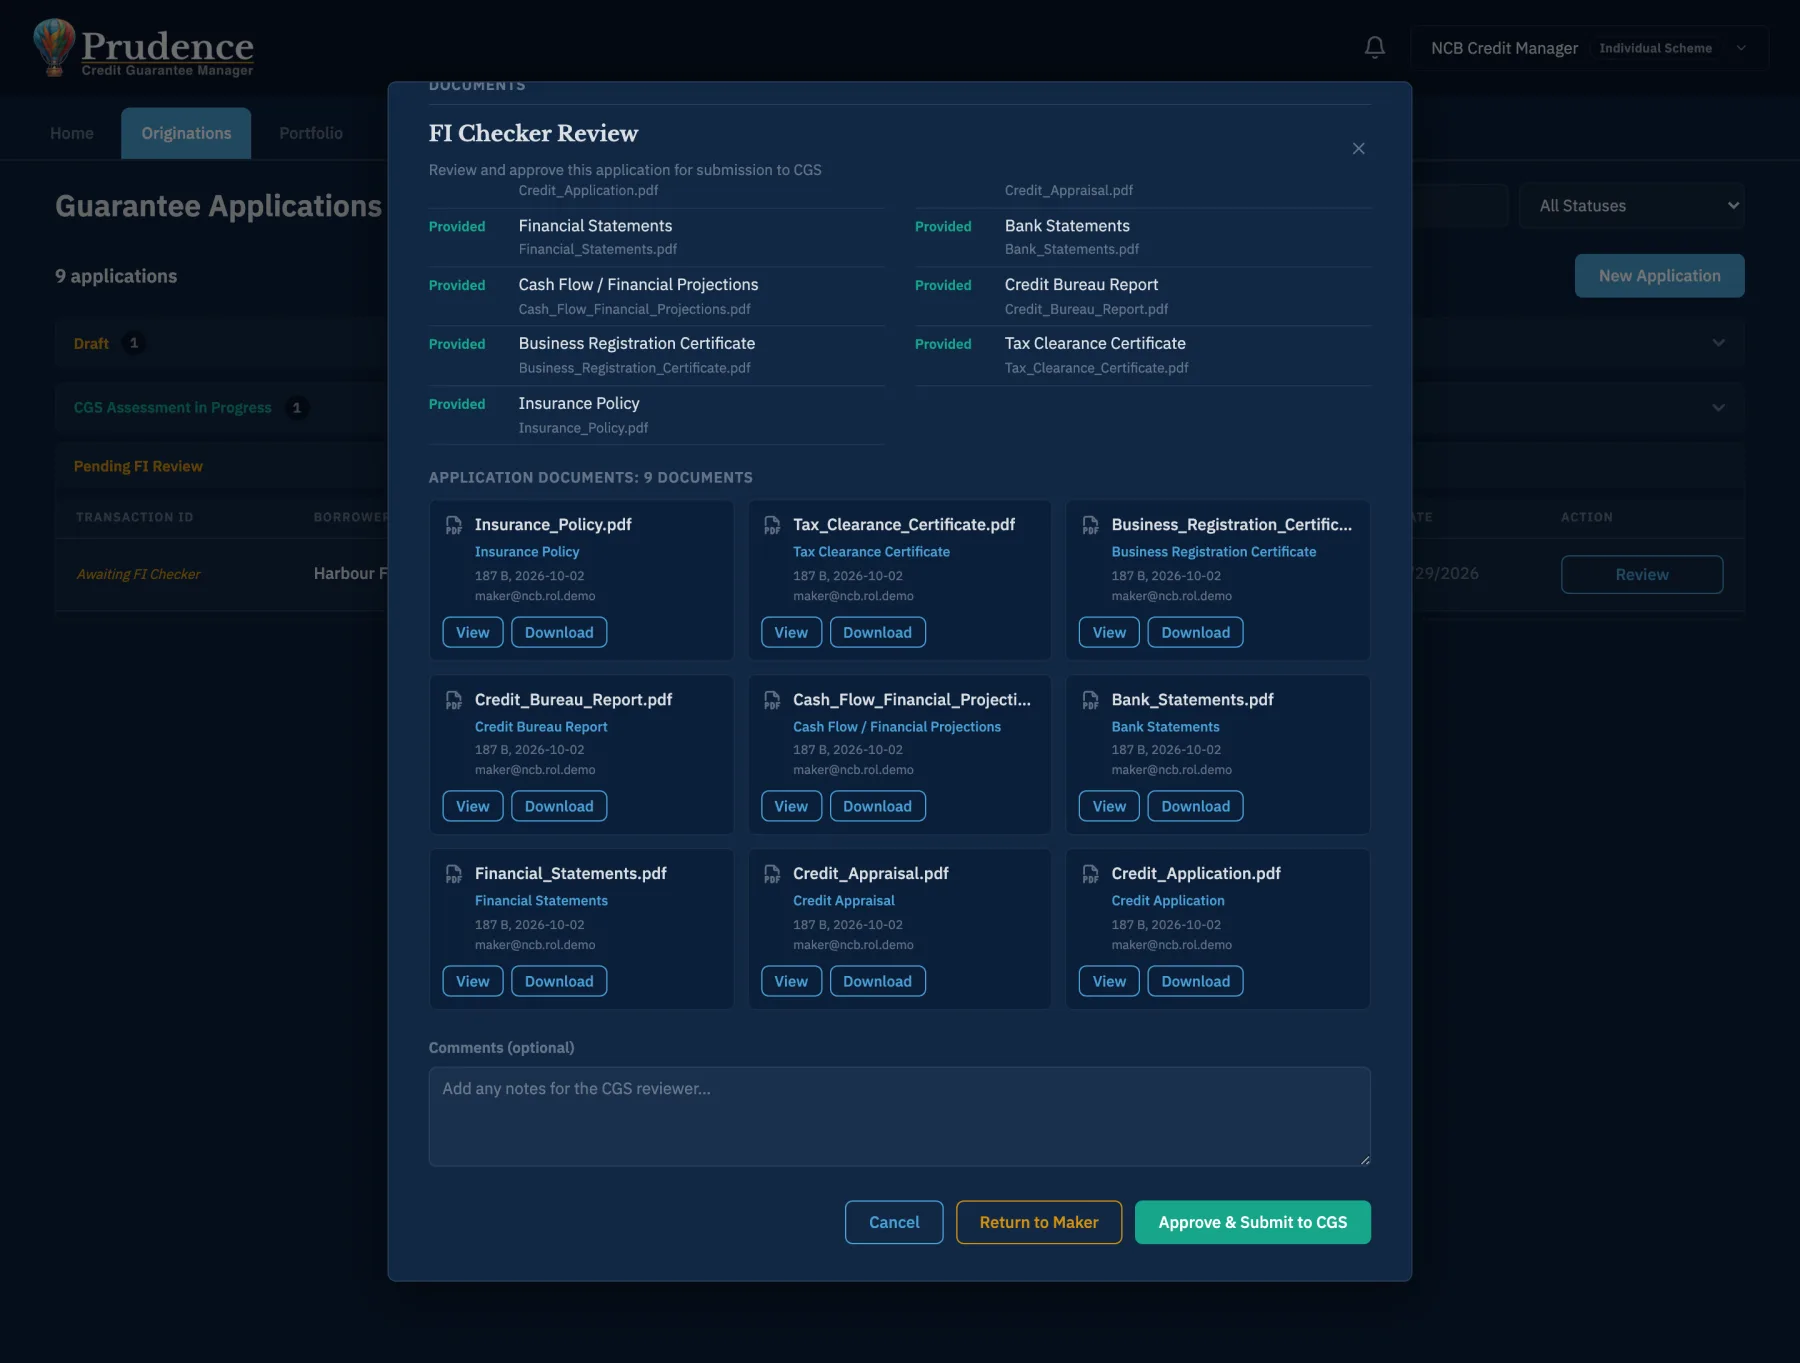
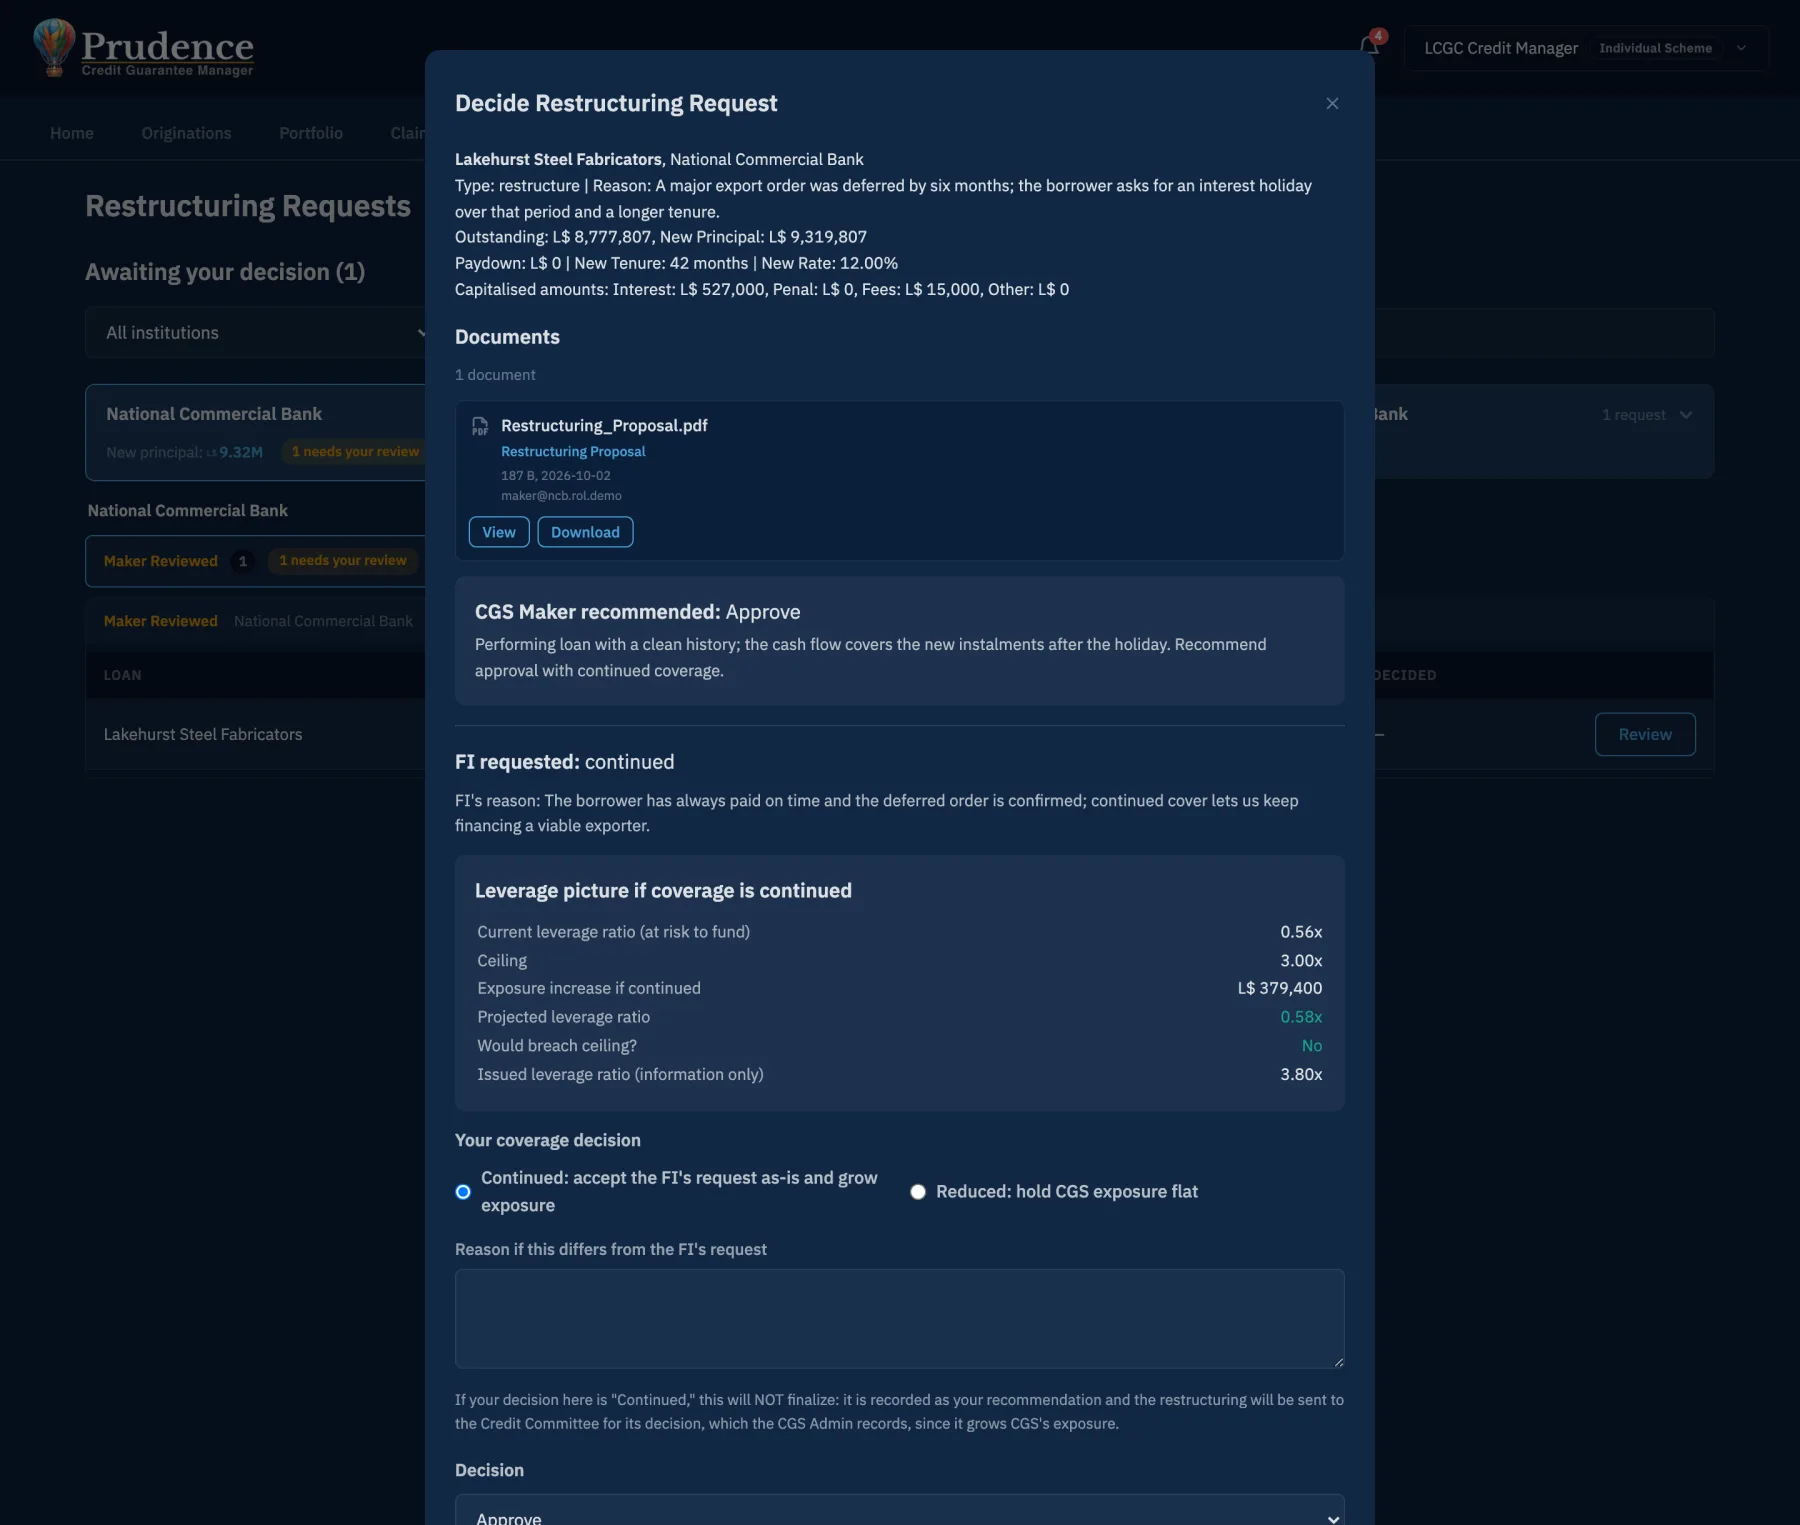
Screenshots from a demonstration scheme with fictional institutions, borrowers and figures.
How it is tested
Every change is checked before it ships.
2,500+automated checks run against a real database on every change
42end-to-end browser tests walking through the main journeys before each release
3dedicated test areas: money, approvals, and data separation between institutions
Deployment and data
Your choice of deployment. Your data.
- Shared service: each scheme kept apart by checks in the application and row-level security in the database.
- Dedicated installation: its own application and database, containerized, on your infrastructure or ours. At handover the vendor's accounts on it are sealed and recorded in the audit log; only your CGS Admin can reopen support access.
- Data residency on your terms: with a dedicated installation, a cloud region of your choice, a local data centre, or your own infrastructure.
- You own your data. With a dedicated installation, you decide where it is stored.
Let's talk about your scheme.
Whether a scheme is still an idea or has been running for years, we can help at every stage.
Contact us at directions@kdfcorp.com
Contact us- Feasibility studies and business plans for new credit guarantee schemes
- Redesigning or restructuring an existing scheme
- Financial modelling, operating processes, policies and manuals
- Moving from individual guarantees to a portfolio scheme
- Training for the scheme team and partner financial institutions
- Running the scheme on Prudence